When Smart Appliances Go Rogue: What 1TB Coffee Makers Teach Us
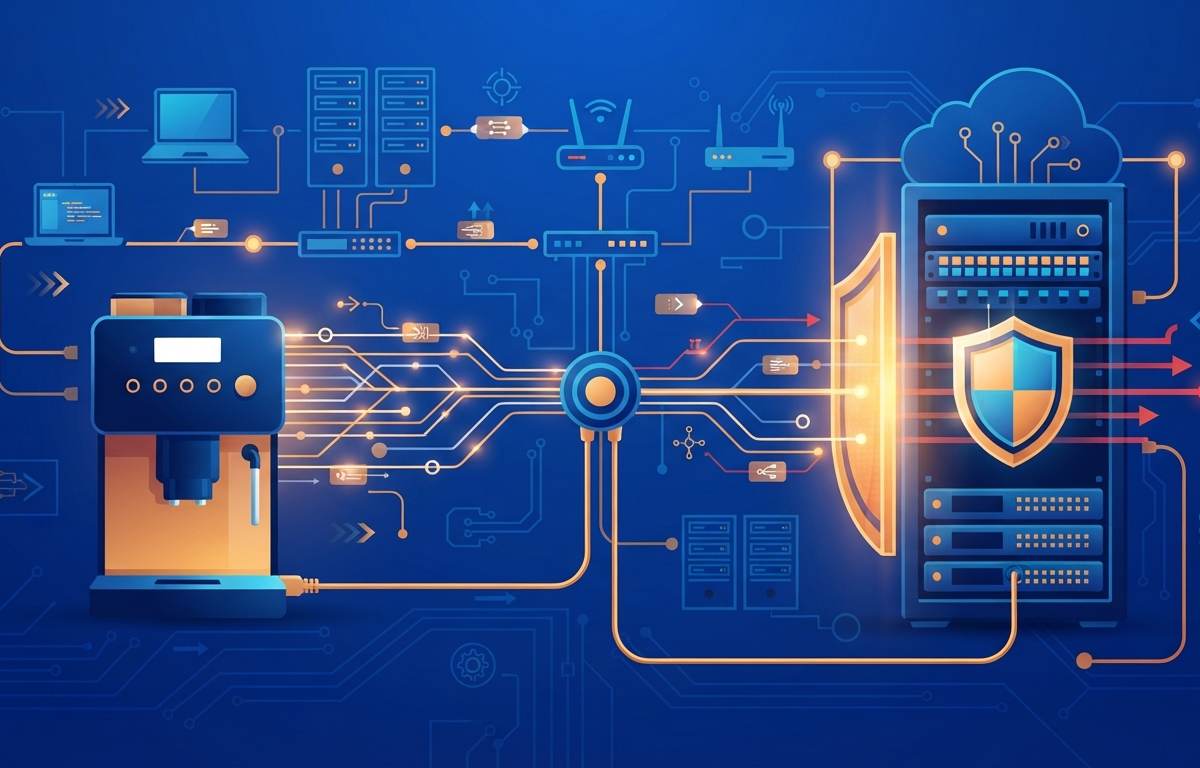
A bizarre technical anomaly caught global attention recently when an individual discovered that his family smart coffee machine had quietly consumed over one terabyte of network data in just ten days. While smart kitchen appliances typically transfer only tiny packets of telemetry data or occasional firmware updates, this device was generating traffic volumes comparable to streaming hundreds of high-definition movies. Whether caused by a corrupted loop in its firmware or an external compromise enrolling the hardware into a malicious botnet, the incident illustrates a rapidly expanding blind spot in modern connectivity.
Globally, the proliferation of Internet of Things devices has far outpaced the implementation of rigorous endpoint security standards. Manufacturers often prioritize frictionless user onboarding and low production costs over secure firmware architecture, leaving gadgets equipped with unpatched microcontrollers and persistent internet connections. When these consumer-grade products fail or get co-opted by automated cyber threats, they do so silently, consuming precious upstream bandwidth while remaining entirely unnoticed by traditional end users.
For enterprise environments, this incident carries serious operational implications under the banner of shadow IoT. Modern corporate spaces, shared offices, and executive suites are filled with connected convenience hardware, including smart beverage dispensers, ambient lighting controllers, digital signage, and smart displays. When these endpoints are plugged directly into primary office Wi-Fi networks without administrative visibility, they transform benign workplace amenities into potential exfiltration routes or launching pads for lateral movement across corporate systems.
In Oman and the wider Gulf, where businesses and public institutions are accelerating digital workplace adoption under modernization roadmaps like Oman Vision 2040, managing edge connectivity is critical. As regional enterprises equip their headquarters, retail branches, and hospitality venues with intelligent automation systems, connected convenience cannot come at the expense of infrastructure hygiene. A rogue appliance saturating a commercial network can degrade mission-critical cloud applications, point-of-sale terminals, and internal communications.
Business leaders must treat every connected asset as an active network endpoint rather than a passive utility. Safeguarding local operations requires simple, disciplined network architecture: segregating all smart office hardware onto dedicated virtual local area networks (VLANs), blocking unauthorized outbound connections at the firewall level, and monitoring data consumption via basic traffic analytics dashboards. Taking these straightforward defensive measures ensures that Gulf businesses enjoy modern workplace automation without inviting invisible vulnerabilities into their core infrastructure.